Privacy by design for in-store AI: cameras, consent and the law
How to run cameras and AI in a store responsibly: GDPR biometric rules, the EU AI Act, CCPA, Illinois BIPA, New York City signage, consent and on-device tracking.
To run cameras and AI in a store responsibly, process as little as you can, keep it on the device where possible, never identify people by their face without explicit, opt-in consent, and tell shoppers plainly what the screen does before they use it. In Europe and the UK the line that matters most is whether a system uniquely identifies people; in the United States, Illinois, California and New York City each add their own consent, notice and signage rules.
This article is a practical overview for retail, CRM and privacy teams. It is not legal advice. Laws differ by country and city, they change, and the details of your set-up matter. Take advice from your own counsel before you deploy.
When does a camera in a store process biometric data?
Under the GDPR, biometric data is personal data "resulting from specific technical processing" of a person's physical, physiological or behavioural characteristics "which allow or confirm the unique identification" of that person. Article 9(1) then prohibits processing "biometric data for the purpose of uniquely identifying a natural person" unless an exception applies, the most common being the person's explicit consent under Article 9(2)(a).
The European Data Protection Board's Guidelines 3/2019 on video devices are the clearest guide to where that line falls in a shop. They set out three tests: the nature of the data, whether it results from specific technical processing, and whether the purpose is to uniquely identify someone. Video footage on its own is not biometric data under Article 9 unless it has been technically processed to help identify an individual.
Their retail examples are worth reading in full:
- A shop that detects age and gender to tailor advertising, without templates to identify anyone, is not processing special category data. It still needs a lawful basis.
- A system that spots the same person re-entering the shop is identifying them, so Article 9 applies "from the start".
- Facial recognition for tailored advertising needs the explicit consent of everyone captured, and is unlawful if it captures passers-by who have not consented, "even if their template is deleted within the shortest possible period".
The UK regulator takes the same line. The ICO's guidance on biometric recognition says that using biometric data to uniquely identify someone is processing special category data, that processing digital photographs does not automatically count as biometric data, that explicit consent is likely to be the most appropriate condition, and that a data protection impact assessment (DPIA) should be completed before a biometric recognition system is used.
What does that mean for try-on and an AI stylist?
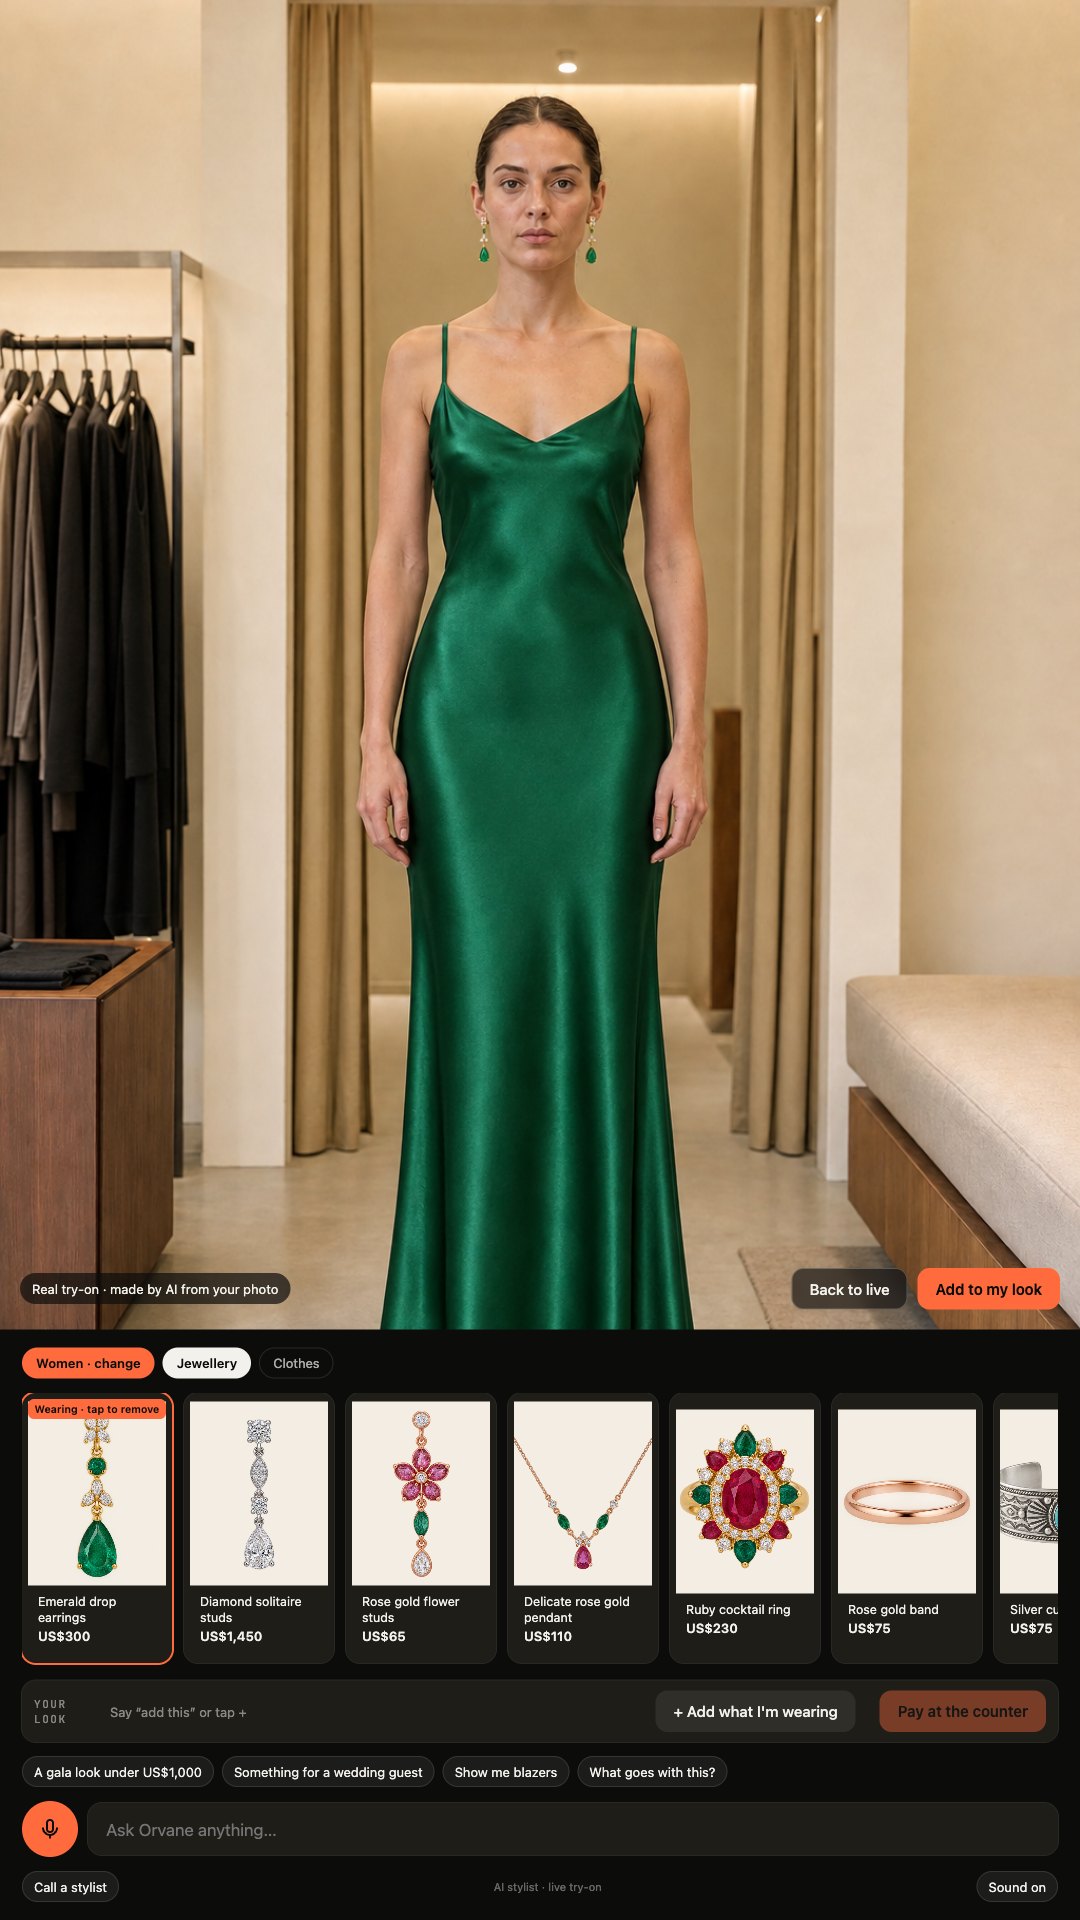
Try-on needs a camera to find a body or a face so a garment or an earring can be placed on it. That is positioning, not identification, and it should stay that way:
- Track, don't template. Locate shoulders, ears and collarbones frame by frame, and keep nothing that could recognise the same person later.
- Keep it on the screen. On-device processing is still covered by data protection law, but there is no stream to intercept, store or reuse.
- Send a picture only when asked. A photo of the look is personal data. Say what happens to it and how long it is kept, and delete it on schedule.
- Remember people only when they ask. Recognising a returning shopper by face is biometric identification. The EDPB's examples show what that needs: explicit consent, an enrolment step the person triggers, and an alternative for anyone who declines.
What does the EU AI Act add?
The AI Act sits on top of the GDPR and adds rules for specific kinds of system.
Biometric categorisation. Article 5(1)(g) prohibits systems that categorise individuals based on biometric data "to deduce or infer their race, political opinions, trade union membership, religious or philosophical beliefs, sex life or sexual orientation". The prohibitions have applied since 2 February 2025. Note the definition in Article 3(40), which excludes categorisation that is "ancillary to another commercial service and strictly necessary for objective technical reasons". Recital 16 gives as an example filters categorising facial or body features used on online marketplaces to let a consumer preview a product on themselves. Whether that reasoning extends to an in-store try-on screen is a question for your lawyers, but the direction is clear: features that exist only to show a product on a person are treated differently from systems that sort people.
Emotion recognition. Article 5(1)(f) prohibits inferring emotions in the workplace and in education. A shop floor is a workplace for its staff, so emotion analysis pointed at employees is off the table. For shoppers it is not prohibited, but emotion recognition systems are listed as high-risk in Annex III. The AI Omnibus, Regulation (EU) 2026/1744, moved the Annex III high-risk obligations to 2 December 2027, as reported by The National Law Review.
Transparency. Under Article 50(3), deployers of an emotion recognition or biometric categorisation system "shall inform the natural persons exposed thereto of the operation of the system". That obligation applies from 2 August 2026, and the information must be given at the latest at the first interaction or exposure.
In its position on "augmented" cameras, the CNIL gives a shop analysing customers' mood to tailor advertising as an example where the balance of interests could tip against the business. The simplest course is not to infer emotions or sensitive traits at all.
What applies in the United States?
California (CCPA as amended by the CPRA)
Civil Code section 1798.140 defines biometric information broadly, and treats "the processing of biometric information for the purpose of uniquely identifying a consumer" as sensitive personal information. The California Attorney General's CCPA guidance explains that consumers can limit how businesses use sensitive personal information, and that a notice at collection must be given at or before the point of collection. The Attorney General and the California Privacy Protection Agency enforce the law.
Illinois (BIPA)
The Biometric Information Privacy Act is the strictest US law in this area and has a private right of action. Section 15 requires a publicly available retention and destruction policy and, before collection, written notice of the purpose and length of term and a written release. Damages are $1,000 per negligent violation or $5,000 per intentional or reckless one. An amendment signed on 2 August 2024 limits repeated collection from the same person by the same method to a single violation and allows electronic signatures for consent, as Greenberg Traurig summarises.
New York City
Since July 2021, retail stores that collect, retain, convert, store or share biometric identifier information must post clear and conspicuous signs near all customer entrances, and may not sell, trade or otherwise profit from that information. Penalties range from $500 to $5,000 per violation, according to Goodwin's summary of the law.
The FTC
The Federal Trade Commission's 2023 policy statement on biometric information lists practices it may treat as unfair, including surreptitious collection and failing to assess foreseeable harms. In December 2023 it announced that Rite Aid would be prohibited from using facial recognition for surveillance for five years.
What should the signage say?
The EDPB recommends layers. The first is a sign at about eye level, seen before people enter the monitored area, giving the purpose, who is responsible, people's rights and the most significant effects, and pointing to fuller information. It should mention anything that could surprise people, such as transfers to third parties or storage periods. Where that is not shown, people "should be able to trust that there is solely a live monitoring (without any data recording or transmission to third parties)".
For a try-on screen, that means a line on the screen at the moment of use, plus a sign or QR code leading to a plain-language privacy page. In New York City, check whether the entrance-sign rule applies.
On-device tracking or recording?
| Approach | What leaves the screen | Main risk |
|---|---|---|
| On-device tracking, nothing stored | Nothing, unless the shopper asks for a photo | Low; mostly about notice and the photo request |
| Recording or streaming video for analytics | Footage of everyone in range | Retention, security, access requests and purpose creep |
| Face templates to recognise returning shoppers | Biometric identifiers | Special category data, explicit consent, BIPA and NYC rules |
A short checklist before you switch a screen on
- Complete a DPIA. Under GDPR Article 35(3)(c), one is required for systematic monitoring of a publicly accessible area on a large scale.
- Give each camera feature a written purpose; remove any feature without one.
- No face templates unless a shopper has enrolled with explicit consent, with an equal alternative.
- Never infer emotions, race, ethnicity or other sensitive traits.
- Process on the device; set a short, enforced retention period for anything that leaves it.
- Ask separately to remember a shopper and to message them; let them see, change or delete what is kept.
- Put a plain line on the screen and a sign in the store, and bind vendors to the same limits.
How Ateliq is designed
In Ateliq, tracking runs on the screen and nothing is recorded, and a line on the glass says so. A frame is sent only when the shopper asks the stylist about a look or asks for a photo, and the photo is deleted after 30 minutes. There is no sign-in. Style profiles exist only for shoppers who opt in, and they can see, change or delete what is kept about them from their phone. Ateliq never infers race, ethnicity or weight. A brand deploying any in-store AI, including ours, should still run its own assessment for its own stores and cities.
Sources
- GDPR Article 9 and Article 35
- EDPB Guidelines 3/2019 on processing of personal data through video devices, version 2.0
- ICO, Biometric data guidance: biometric recognition
- CNIL, Caméras dites « augmentées » dans les espaces publics
- EU AI Act: Article 3, Article 5, Article 50, Recital 16, Annex III
- The National Law Review, EU Digital Omnibus on AI enters into force
- California Civil Code section 1798.140 and California Attorney General, CCPA
- 740 ILCS 14/15 and Greenberg Traurig on the 2024 BIPA amendment
- Goodwin on New York City's biometric identifier law
- FTC policy statement on biometric information and FTC Rite Aid press release
Questions people ask
Is a virtual try-on camera processing biometric data under the GDPR?
Under EDPB guidance, camera images become special category biometric data when they are technically processed to uniquely identify a person. Tracking a body or face only to place a product on it, without templates that could recognise the same person later, is positioning rather than identification, though it is still personal data processing. This is not legal advice.
Does the EU AI Act ban emotion recognition in shops?
Article 5(1)(f) bans inferring emotions in workplaces and education, so it applies to store staff. Emotion recognition aimed at shoppers is not prohibited but is listed as high-risk in Annex III, and from 2 August 2026 deployers must inform the people exposed to it.
What signage does an in-store AI screen need?
The EDPB recommends a first-layer sign at about eye level giving the purpose, who is responsible, people's rights and the main effects, pointing to fuller information. In New York City, stores that collect biometric identifier information must post signs near all customer entrances.